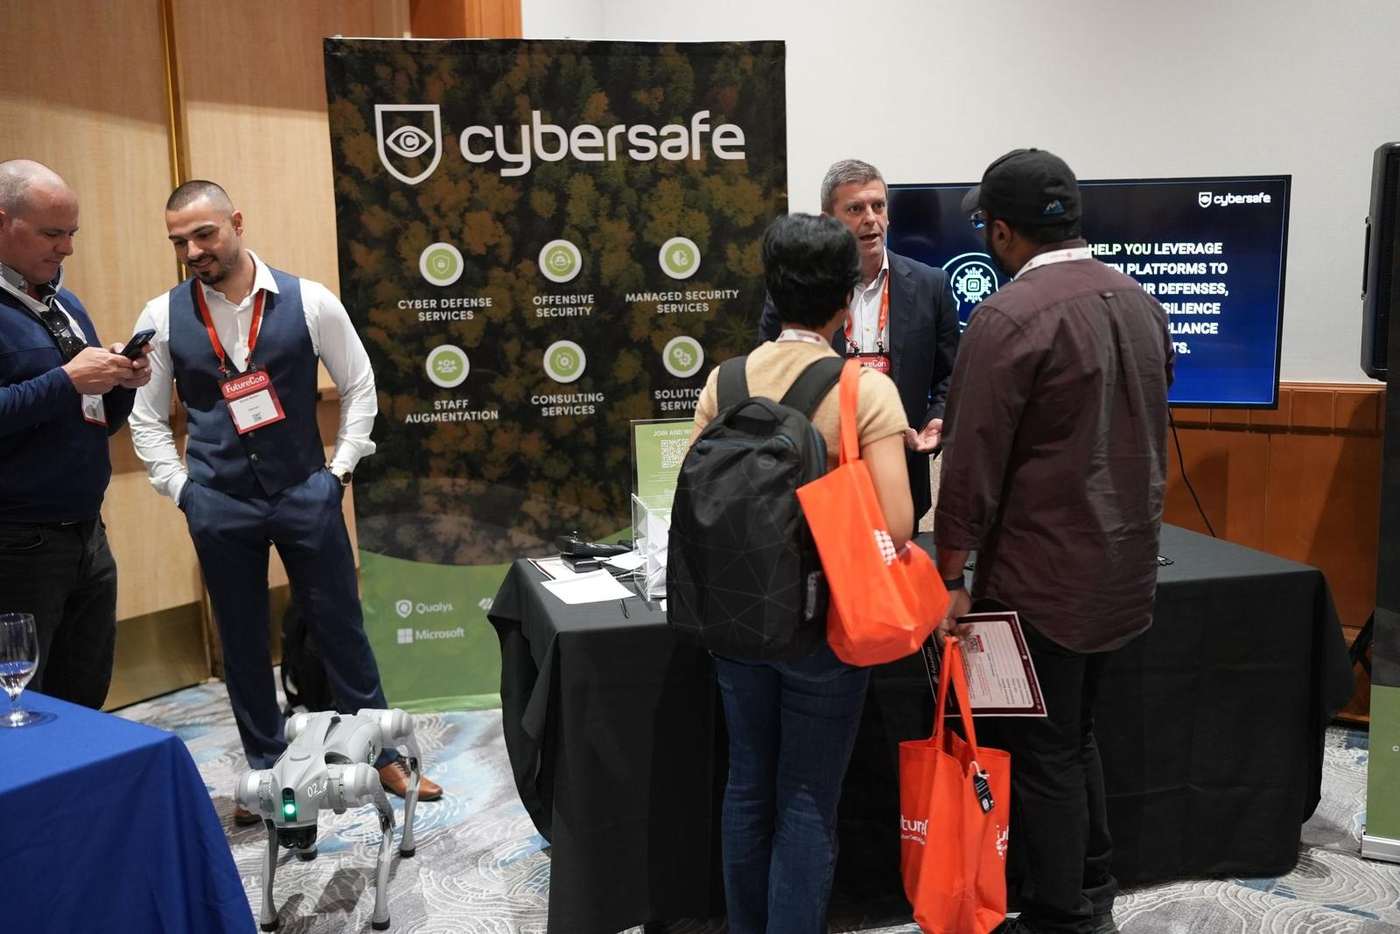
New: CyberSafe CEO Dinis Fernandes keynoted on AI cybersecurity challenges at FutureCon Vancouver 2026.Read the article →
Canada Managed security for regulated organizations

Enterprise cyber defense, run by people who do it every day.

CyberSafe operates 24/7 detection and response, offensive testing and compliance programs for Canadian banks, utilities, hospitals, manufacturers and government teams. Our SOC has been on shift around the clock since 2016.

  • 150+ clients
  • 60+ security professionals
  • 24/7 SOC since 2016
  • ISO 27001 aligned delivery
SOC · LIVE WEST VANCOUVER · 24/7
Events analysed
4.2M
last 24h
Alerts triaged
318
94% auto-enriched
Escalated
3
MTTA 6 min
Alert volume24h · by hour
HighCredential stuffing · VPN gatewayContained
MediumSuspicious OAuth consent · M365Investigating
LowCVE match in Feed · edge firewallTicket opened
Splunk ESSentinelCrowdStrikeCortex XDR
Illustrative snapshot
Trusted by security teams in financial services, energy, pharma, government and technology
Ferring Pharmaceuticals EDP IWG BNP Paribas CGD Luz Saúde

Five practices. One accountable team.

Most clients start with managed detection from our SOC, then add offensive testing, compliance work or embedded specialists as the program matures.

All services & solutions

Built for organizations that cannot afford to lose a day

We are not here to sell licences or hours. Most clients come to us with tools already in place and need someone to make the program work properly.

10+

Years running a SOC well

The hard part is not the technology. It is keeping good analysts on shift for years, tuning detection so the queue stays survivable, and knowing what to escalate.

60+

Specialists, not generalists

Pen testers who write their own tooling. GRC consultants who have worked the other side of the audit table. Analysts who rotate into threat hunting and detection engineering.

80+

Audits shepherded through

ISO 27001, SOC 2, PCI DSS, PIPEDA and provincial privacy regimes. We know which controls assessors care about and which ones they wave through.

30+

Vendor partners, zero lock-in

Splunk or Sentinel, CrowdStrike or Cortex, Palo Alto or Fortinet. We pick the tools that fit each environment instead of reselling one stack.

From first call to live monitoring in four to eight weeks

Most onboardings follow this shape. Banks and federal clients take longer because of the compliance gates we clear together.

Step 01

Discovery

Attack-surface mapping, log review and stakeholder interviews. We benchmark against the framework your auditor cares about: NIST CSF, ISO 27001, PCI DSS or OSFI B-13.

Gap analysisAsset discovery
Weeks 1–3
Step 02

Stack design

SIEM, EDR, email, identity and network controls chosen for your environment. We integrate what you already own before recommending anything new.

SIEM / SOARZero Trust
Weeks 3–5
Step 03

Live monitoring

Once ingestion is verified and runbooks are signed off, the SOC goes live. Analysts triage, hunt for what rules miss, and escalate only what matters.

24/7 SOCIncident response
Weeks 5–8
Step 04

Continuous improvement

Quarterly pen tests, annual red team, audit prep and awareness training. The work shifts from putting out fires to making sure new ones do not start.

Red teamCompliance
Ongoing

Two platforms we built for our own SOC, now available to clients

Both started as internal tooling for our analysts. Clients kept asking for them, so we turned them into products. We still use them every day.

Threat intelligence

CyberSafe Feed

Threat Intelligence Platform

Aggregates, normalises and scores indicators from open-source, commercial and our own incident telemetry, then pushes the result straight into your SIEM.

  • Millions of indicators processed daily with confidence scoring
  • Native connectors for Splunk, Sentinel, QRadar and InsightIDR
  • Dark-web monitoring and brand protection alerts
Explore CyberSafe Feed
Awareness

CyberSafe Phish

Phishing Simulation & Awareness Platform

Realistic phishing simulations that test how people actually respond, track awareness maturity over time, and reduce human risk without shaming anyone.

  • Campaign templates built on real Canadian lures
  • Automated micro-training for people who click
  • Board-ready reporting on click, report and repeat rates
Explore CyberSafe Phish

Engagements we can talk about publicly

Most of our work is under NDA. These three clients gave us permission to name them. Reference calls with comparable organizations are available on request.

Pharmaceuticals · 50+ countries

Ferring Pharmaceuticals

Next-generation firewall deployment and managed security across Ferring's global operations, with centralised policy and regional customisation for local compliance.

  • Consistent posture across 50+ countries
  • Compliance assessment overhead cut by 60%
NGFWManaged SecurityDLP
Energy · 29 countries

EDP

Dedicated CyberSafe professionals across SOC operations, cloud security, SIEM engineering and change management for one of the world's largest energy companies.

  • Multi-year embedded team across four disciplines
  • Coverage for operations in 29 countries
Staff AugmentationSOCCloud Security
Workplace · 120+ countries

IWG

24/7 managed detection and response across 4,000+ locations, running Microsoft Sentinel and Defender for endpoint, identity, cloud and vulnerability management.

  • 4,000+ workspaces monitored around the clock
  • Single Sentinel platform across 120+ countries
MDR 24/7Microsoft SentinelVulnerability mgmt

Latest from the CyberSafe team

Breach analysis, threat intelligence and company news, written by the analysts and consultants who do the work.

All articles

Tell us what you are trying to fix. We will tell you honestly whether we are a fit.

A 30-minute scoping call with a pre-sales engineer, not a salesperson. We look at what you already have in place before recommending anything.

Book a scoping call Response within one business day. NDA available on request.

Quick contact

Tell us a little about your organization and what you need. A specialist replies within one business day.

Reply within one business day NDA on request No obligation

Thanks. Your message is with the team.

A CyberSafe specialist will reply within one business day. If this is an active incident, email info@cybersafe.global with "URGENT" in the subject line.